

Preparing for a cybersecurity role in 2026 requires more than memorizing definitions. Candidates are expected to understand security principles, network protection, cloud environments, application security, and practical troubleshooting. Professionals preparing for roles involving Python coding problems, and Java Backend Developer positions may also face security-related questions because modern development teams increasingly work with secure APIs, authentication, databases, and cloud infrastructure.
For candidates targeting technical roles, security knowledge can complement skills in React components, and asp net core. This guide covers commonly asked cybersecurity interview questions along with practical answers for freshers and experienced professionals.
What Are Cybersecurity Concepts?
Cyber security concepts are the fundamental principles and practices used to protect systems, applications, networks, devices, and data from unauthorized access, attacks, and security threats.
Some important concepts include:
- Confidentiality, integrity, and availability (CIA)
- Authentication and authorization
- Encryption and hashing
- Firewalls and intrusion detection
- Vulnerability management
- Access control
- Incident response
- Risk assessment
- Security monitoring
A strong understanding of these concepts helps candidates answer both theoretical and scenario-based interview questions.
1. What Is Cybersecurity?
Cybersecurity is the practice of protecting computers, networks, applications, cloud infrastructure, and data from unauthorized access, cyberattacks, damage, or disruption.
Organizations use multiple security controls, including firewalls, encryption, identity management, endpoint protection, vulnerability scanning, and security monitoring.
Interview Tip: Explain cybersecurity as a combination of people, processes, and technologies rather than only describing it as antivirus or firewall protection.
2. What Is the CIA Triad?
The CIA triad represents three fundamental cybersecurity principles:
| Principle | Meaning | Example |
| Confidentiality | Prevents unauthorized access to information | Encryption |
| Integrity | Prevents unauthorized modification | File hashing |
| Availability | Keeps systems and services accessible | Backup systems |
A security professional should balance all three principles when designing security controls.
3. What Is the Difference Between Authentication and Authorization?
Authentication verifies who a user is, while authorization determines what that authenticated user is allowed to access.
For example, when a user logs into an application, their username and password authenticate their identity. Permissions assigned to their account determine whether they can view, edit, or delete specific resources.
4. What Is a Firewall?
A firewall is a security mechanism that monitors and controls incoming and outgoing network traffic according to predefined rules.
Firewalls can be implemented as:
- Network firewalls
- Host-based firewalls
- Cloud firewalls
- Web application firewalls
They can help block unauthorized connections while allowing legitimate traffic.
5. What Are Common Network Security Questions Asked in Interviews?
Network security questions often test a candidate’s understanding of network protocols, traffic filtering, attacks, and defensive mechanisms.
Common areas include:
- TCP/IP
- DNS and DHCP
- Firewalls
- VPNs
- Network segmentation
- IDS and IPS
- Port scanning
- DDoS attacks
- Secure communication protocols
Example Question: What Is the Difference Between IDS and IPS?
An Intrusion Detection System (IDS) monitors network activity and generates alerts when suspicious behavior is detected.
An Intrusion Prevention System (IPS) can actively block or prevent suspicious traffic.
| Feature | IDS | IPS |
| Primary function | Detects threats | Detects and prevents threats |
| Response | Generates alerts | Can block traffic |
| Deployment | Often monitors traffic | Usually positioned inline |
| Main purpose | Visibility | Protection |
6. What Is an Ethical Hacker?
An ethical hacker is a cybersecurity professional who legally tests systems, networks, or applications to identify vulnerabilities before malicious attackers can exploit them.
During an ethical hacking interview, candidates may be asked about penetration testing, reconnaissance, vulnerability assessment, authentication weaknesses, and responsible disclosure.
Ethical hacking must always be performed with proper authorization and clearly defined scope.
7. What Is Penetration Testing?
Penetration testing is an authorized security assessment in which testers simulate potential attacks against systems or applications to identify exploitable weaknesses.
A typical penetration-testing process includes:
- Planning and defining scope
- Reconnaissance
- Vulnerability identification
- Controlled validation
- Risk assessment
- Reporting
- Remediation recommendations
8. What Is Vulnerability?
A vulnerability is a weakness in software, hardware, configuration, or a process that could potentially be exploited by an attacker.
Examples include:
- Outdated software
- Weak passwords
- Improper access controls
- Misconfigured cloud storage
- Unpatched systems
- Insecure APIs
9. What Is the Difference Between a Threat, Vulnerability, and Risk?
These terms are related but have different meanings.
| Term | Definition | Example |
| Threat | Potential cause of harm | Attacker |
| Vulnerability | Security weakness | Unpatched server |
| Risk | Potential impact from a threat exploiting a vulnerability | Data breach |
| Control | Measure used to reduce risk | Security patch |
Understanding this distinction is especially useful during a security analyst interview.
10. What Is SQL Injection?
SQL injection is an application security vulnerability where untrusted input is improperly incorporated into SQL queries, potentially allowing an attacker to manipulate database operations.
Developers can reduce the risk by using:
- Parameterized queries
- Prepared statements
- Input validation
- Proper database permissions
- Secure ORM practices
Understanding database security is useful when discussing SQL joins, database access, and backend application development.
11. What Are SQL Joins?
SQL joins combine related data from multiple database tables using a common relationship.
The commonly used joins include:
- INNER JOIN
- LEFT JOIN
- RIGHT JOIN
- FULL OUTER JOIN
For cybersecurity professionals, understanding SQL is useful when investigating logs, analyzing security events, and querying security-related datasets.
12. What Is Cross-Site Scripting (XSS)?
Cross-Site Scripting, or XSS, is a web security vulnerability in which malicious scripts can be injected into web pages and executed in another user’s browser.
Common prevention techniques include:
- Output encoding
- Input validation
- Content Security Policy
- Secure framework defaults
- Avoiding unsafe HTML rendering
13. What Is API Security?
API security involves protecting APIs from unauthorized access, data exposure, abuse, and manipulation.
Important API security practices include:
- Strong authentication
- Authorization checks
- HTTPS
- Input validation
- Rate limiting
- Secure token management
- Logging and monitoring
Candidates working with API development should understand how authentication and authorization are applied to API endpoints.
14. What Security Risks Should Be Considered During API Development?
During API development, developers and security professionals should consider authentication, authorization, input validation, sensitive-data exposure, rate limiting, and secure error handling.
For example, an API should not rely solely on authentication. It should also verify whether the authenticated user has permission to access the requested resource.
15. What Is Cloud Security?
Cloud security refers to practices used to protect cloud-based applications, infrastructure, identities, workloads, and data.
Security responsibilities can include:
- Identity and access management
- Encryption
- Network security
- Logging
- Monitoring
- Configuration management
- Vulnerability management
16. What Security Considerations Are Important in AWS?
AWS cloud environments require careful management of identities, permissions, networking, storage, encryption, monitoring, and configuration.
Common areas interviewers may ask about include:
- IAM
- Security Groups
- Network ACLs
- CloudTrail
- CloudWatch
- S3 security
- Encryption
- VPC security
The principle of least privilege is particularly important when assigning permissions.
17. What Is the Principle of Least Privilege?
The principle of least privilege means giving users, applications, and services only the permissions they need to perform their required tasks.
For example, an application that only needs to read database records should not receive permissions to delete or modify those records.
This reduces the potential impact if an account or service is compromised.
18. What Are DevOps Tools and Why Are They Relevant to Cybersecurity?
Modern security teams often work closely with development and operations teams. DevOps tools can support automated testing, deployment, monitoring, and security checks throughout the software development lifecycle.
Examples include:
- Git
- Docker
- Kubernetes
- Jenkins
- CI/CD platforms
- Infrastructure-as-Code tools
- Cloud monitoring platforms
This approach is commonly associated with DevSecOps, where security practices are integrated into development and deployment processes.
19. What Are Git Commands Commonly Used by Developers?
Git commands help developers manage source code and collaborate on software projects.
| Git Command | Purpose |
| git clone | Copies a repository |
| git status | Shows repository status |
| git add | Stages changes |
| git commit | Records changes |
| git pull | Retrieves and integrates remote changes |
| git push | Uploads commits to a remote repository |
| git branch | Manages branches |
| git merge | Combines branches |
From a security perspective, teams should also protect repositories, credentials, secrets, and access permissions.
20. What Are Kubernetes Pods?
Kubernetes pods are the smallest deployable units in Kubernetes. A pod can contain one or more containers that share networking and storage resources.
Security considerations for Kubernetes include:
- Role-Based Access Control
- Network policies
- Secrets management
- Container image security
- Resource restrictions
- Pod security controls
21. What Are Docker Containers?
Docker containers package an application and its dependencies into an isolated environment so that it can run consistently across different systems.
Security practices include:
- Using trusted base images
- Scanning images for vulnerabilities
- Avoiding unnecessary root privileges
- Keeping images updated
- Limiting container permissions
22. What Is a Security Operations Center (SOC)?
A Security Operations Center is a team or function responsible for monitoring, detecting, investigating, and responding to cybersecurity threats.
SOC teams commonly work with:
- SIEM platforms
- Endpoint security
- Network monitoring
- Threat intelligence
- Incident response tools
- Security alerts
23. What Questions Can Be Asked in a Security Analyst Interview?
A security analyst interview may include questions about incident response, log analysis, vulnerability management, SIEM tools, access control, and threat detection.
Example Scenario
Question: A user reports that their account may have been compromised. What would you do?
Answer: First, I would verify the alert or suspicious activity by reviewing authentication and system logs. I would secure the account according to the organization’s incident-response process, investigate unusual access, identify potentially affected systems or data, and document the incident. Further actions would depend on the organization’s established procedures and severity assessment.
24. What Is an Incident Response?
Incident response is the structured process used to identify, contain, investigate, eradicate, and recover from security incidents.
A common lifecycle is:
- Preparation
- Detection and analysis
- Containment
- Eradication
- Recovery
- Lessons learned
25. How Do You Prepare for Cybersecurity Interviews in 2026?
A strong preparation strategy should combine theory with practical scenarios.
Focus on:
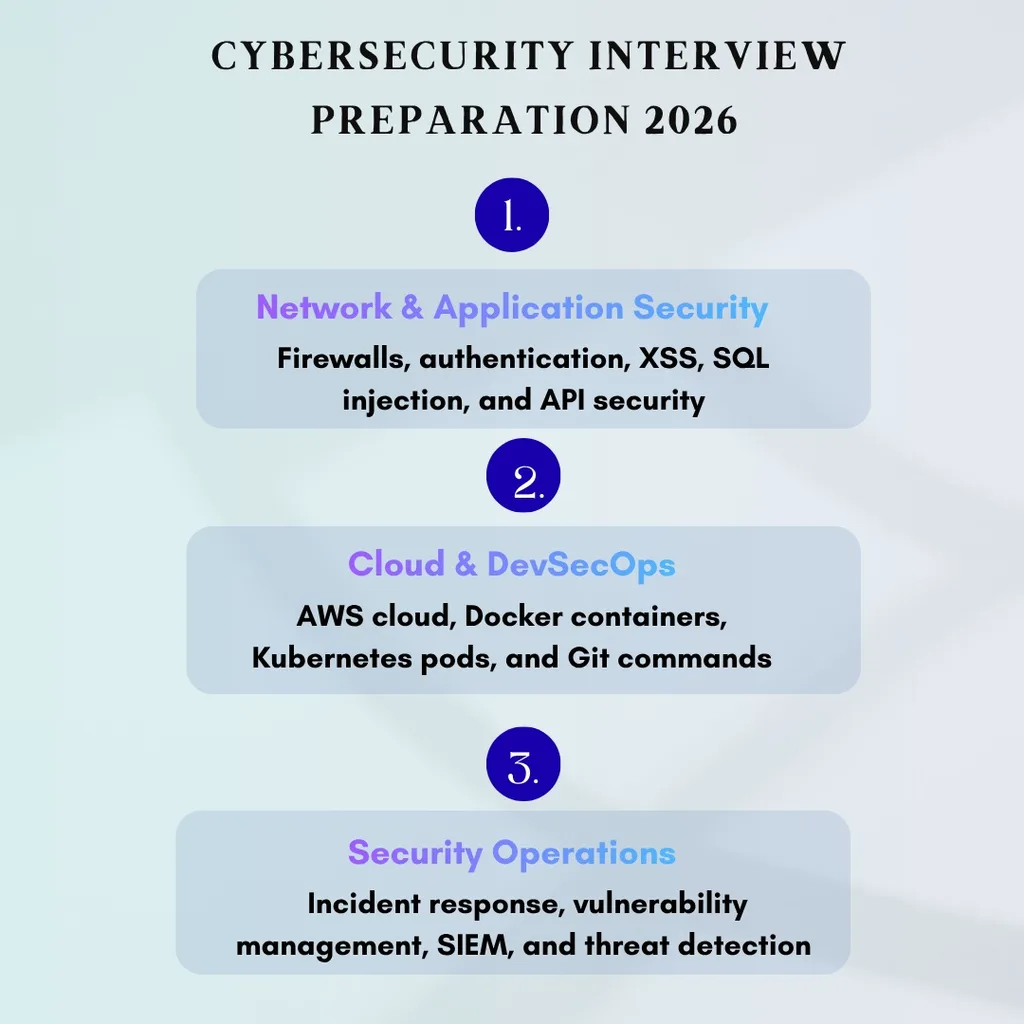
- Cybersecurity fundamentals: CIA triad, authentication, authorization, encryption
- Network security: TCP/IP, firewalls, VPNs, IDS/IPS
- Application security: XSS, SQL injection, API security
- Cloud security: IAM, permissions, logging, encryption
- DevSecOps: Git, Docker, Kubernetes, CI/CD
- Incident response: detection, investigation, containment, recovery
- Security analysis: logs, alerts, vulnerabilities, risk assessment
Quick Preparation Checklist
| Area | Topics to Prepare |
| Fundamentals | CIA triad, authentication, authorization |
| Network | TCP/IP, DNS, firewalls, IDS/IPS |
| Application | XSS, SQL injection, API security |
| Cloud | IAM, encryption, monitoring |
| DevSecOps | Git, Docker, Kubernetes, CI/CD |
| Operations | SIEM, incident response, threat detection |
Conclusion
Cybersecurity interviews in 2026 increasingly test practical knowledge across networks, applications, cloud environments, and modern development workflows. Candidates should understand core security principles while also becoming familiar with technologies such as AWS cloud, Docker containers, Kubernetes pods, Git commands, DevOps tools, and API development.
Whether you are preparing for an entry-level cybersecurity position, an ethical hacking interview, a security analyst interview, or a broader technical role, practicing scenario-based questions can help you communicate your technical reasoning more confidently. Understanding cyber security concepts, application vulnerabilities, cloud security, and incident response will also help you handle questions that go beyond basic definitions.
Frequently Asked Questions
1. What are the most important cybersecurity interview topics for 2026?
Candidates should prepare cybersecurity fundamentals, network security, application security, cloud security, identity management, incident response, vulnerability management, and DevSecOps.
2. Are cybersecurity interviews suitable for freshers?
Yes. Freshers can be asked fundamental questions about networking, operating systems, security concepts, authentication, encryption, common vulnerabilities, and basic incident scenarios.
3. What is the difference between cybersecurity and information security?
Cybersecurity generally focuses on protecting digital systems, networks, applications, and data from cyber threats. Information security interview questions may cover the broader protection of information, including confidentiality, integrity, availability, policies, processes, and physical security.
4. Do cybersecurity professionals need programming knowledge?
Programming is not mandatory for every cybersecurity role, but basic programming can be highly useful. Knowledge of languages such as Python, JavaScript, Java, SQL, or scripting languages can help with automation, security testing, log analysis, and application security.
5. How can I improve my cybersecurity interview preparation?
Practice both conceptual and scenario-based questions. Review networking, operating systems, cloud platforms, application security, incident response, and common security tools. Also prepare to explain how you would investigate and respond to realistic security incidents.
